The Ransomware Economy Expands: Activity Got Bigger, Broader and More Fragmented
Executive Summary
Q3 2026 marked a material acceleration in public ransomware victims. CyberMon DRI telemetry recorded 2,942 victims, up from 2,373 in Q2, while the number of active groups increased from 89 to 106. That represents a 24.0% quarter-over-quarter increase in victims and a 19.1% increase in active groups.
The quarter was not simply busier; it was more fragmented. Thirty-four groups were first observed during Q3 versus 24 in Q2. Manufacturing became the largest affected sector in Q3, while Technology, Healthcare and Financial Services all expanded meaningfully. The United States remained the dominant geography by a wide margin.
India deserves specific attention. The Q3 India dataset contains 75 ransomware victims explicitly geolocated to India across the full quarter: 24 in July, 27 in August and 24 in September. Manufacturing leads with 18 victims, followed by Technology with 15. TheGentlemen is the most active group in the India dataset with 16 victims, followed by Krybit with 9 and Vexy Ransomware with 5.
| Metric | Q2 2026 | Q3 2026 | Change |
|---|---|---|---|
| Claimed victims | 2,373 | 2,942 | +24.0% |
| Active groups | 89 | 106 | +19.1% |
| Countries hit | 107 | 124 | +15.9% |
| Sectors hit | 13 | 13 | No change |
| New groups first seen | 24 | 34 | +41.7% |
1. Q3 2026: The Quarter in View
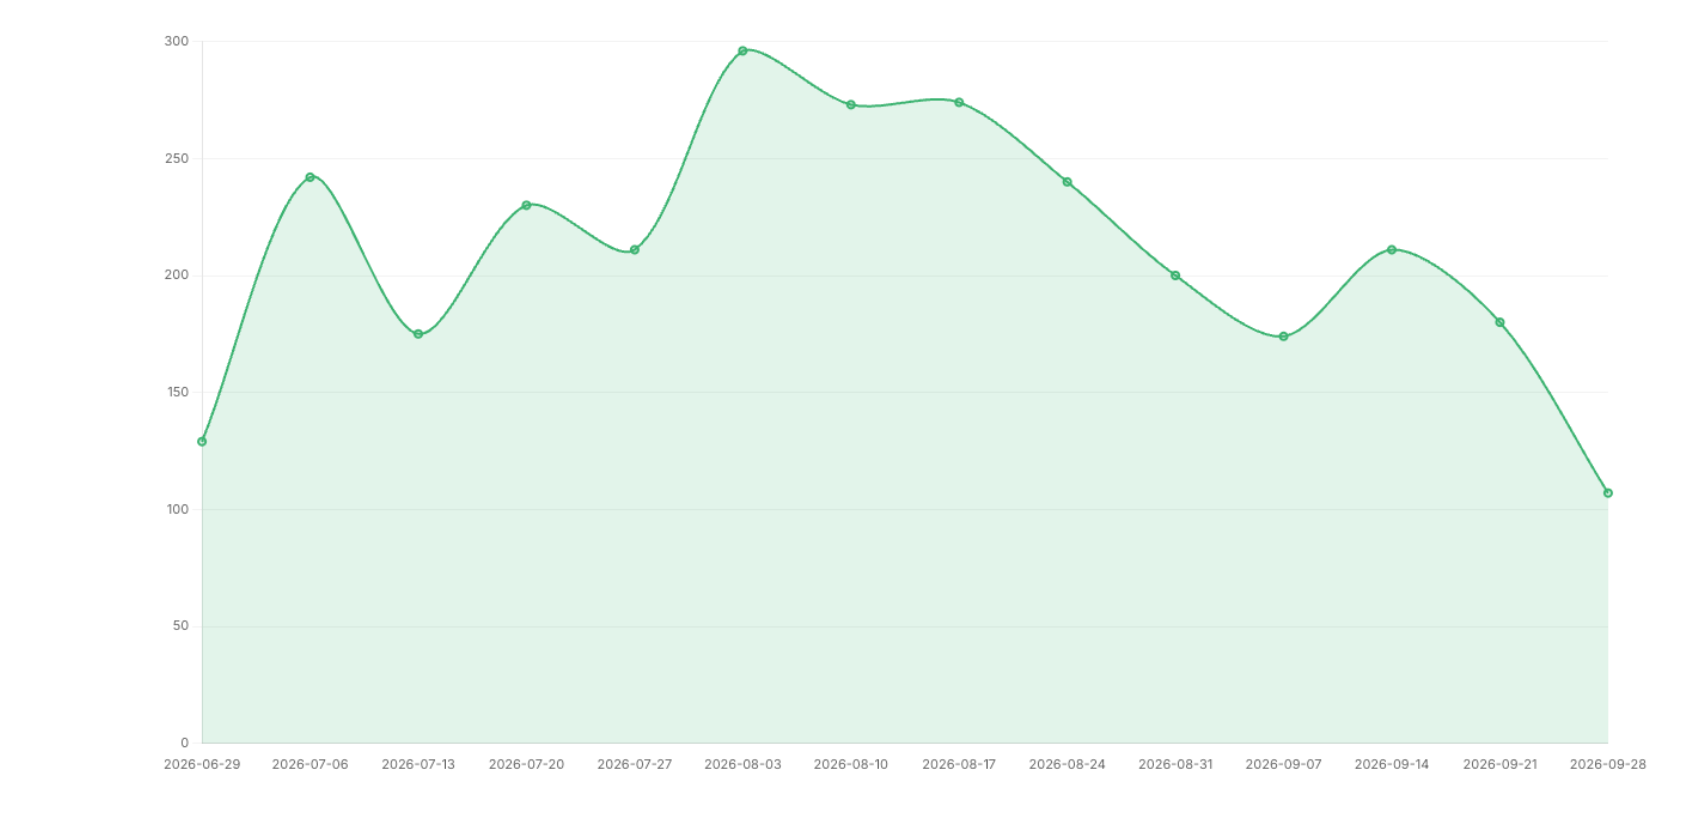
Ransomware victim count rose sharply through July and reached its strongest weekly level in early August, approaching 300 victims worldwide in a week. Activity then moderated through late August and early September, rebounded around mid-September, and declined again at quarter-end. The pattern suggests multiple overlapping campaigns rather than a single sustained spike.
Sector exposure shifted toward manufacturing
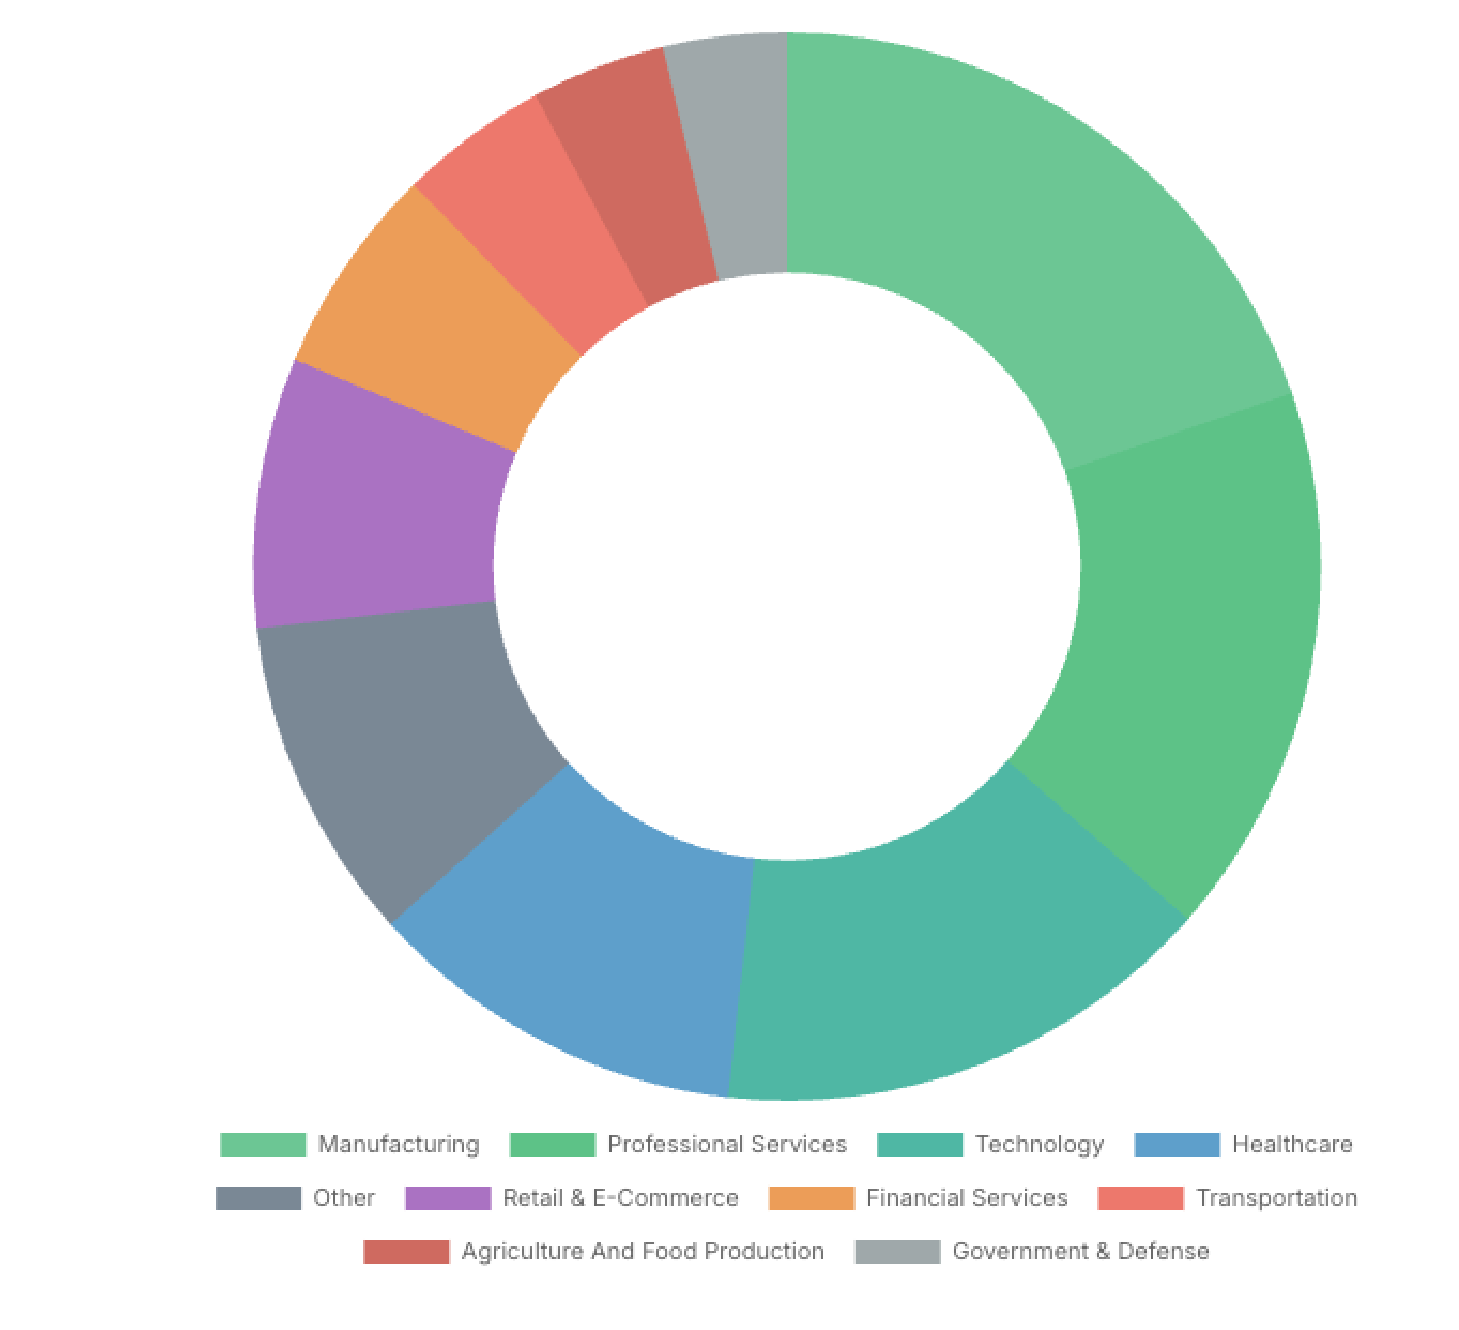
Manufacturing led Q3 with 480 victims, followed by Professional Services (407), Technology (372), Healthcare (281) and Retail & E-Commerce (199). Financial Services recorded 154 victims. Compared with Q2, Manufacturing rose from 394 to 480 (+21.8%), Technology from 260 to 372 (+43.1%), Healthcare from 204 to 281 (+37.7%), and Financial Services from 107 to 154 (+43.9%). Professional Services moved in the opposite direction, falling from 519 to 407 (-21.6%).
Actor concentration remained high despite ecosystem fragmentation
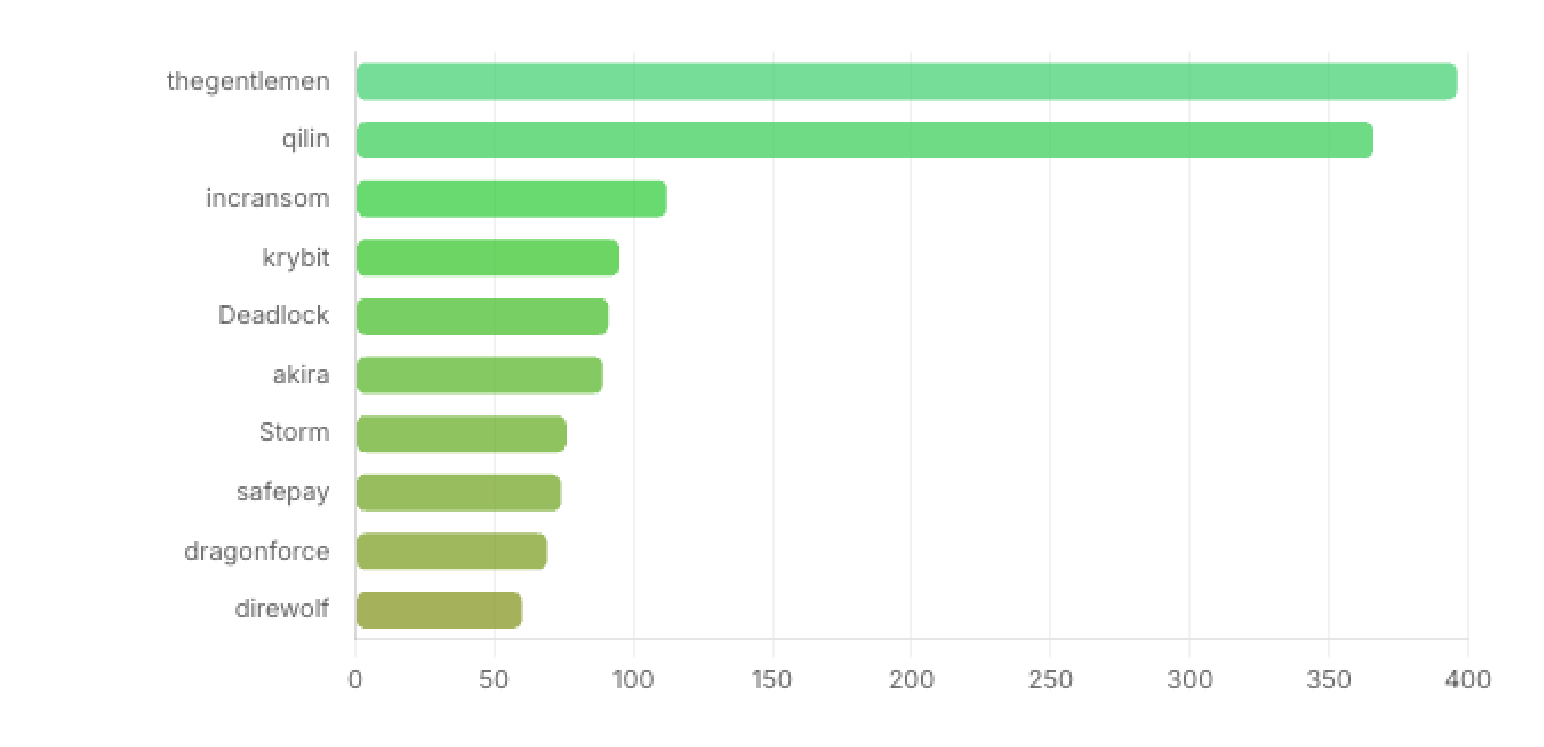
The top-group view shows TheGentlemen and Qilin far ahead of most peers, with Incransom, Krybit, LockBit5, Akira, Storm, SafePay, DragonForce and Direwolf forming the next tier. The important strategic signal is the coexistence of a few high-volume operators with a long tail of newly appearing brands.
Geography: the US remains the centre of ransomware activity
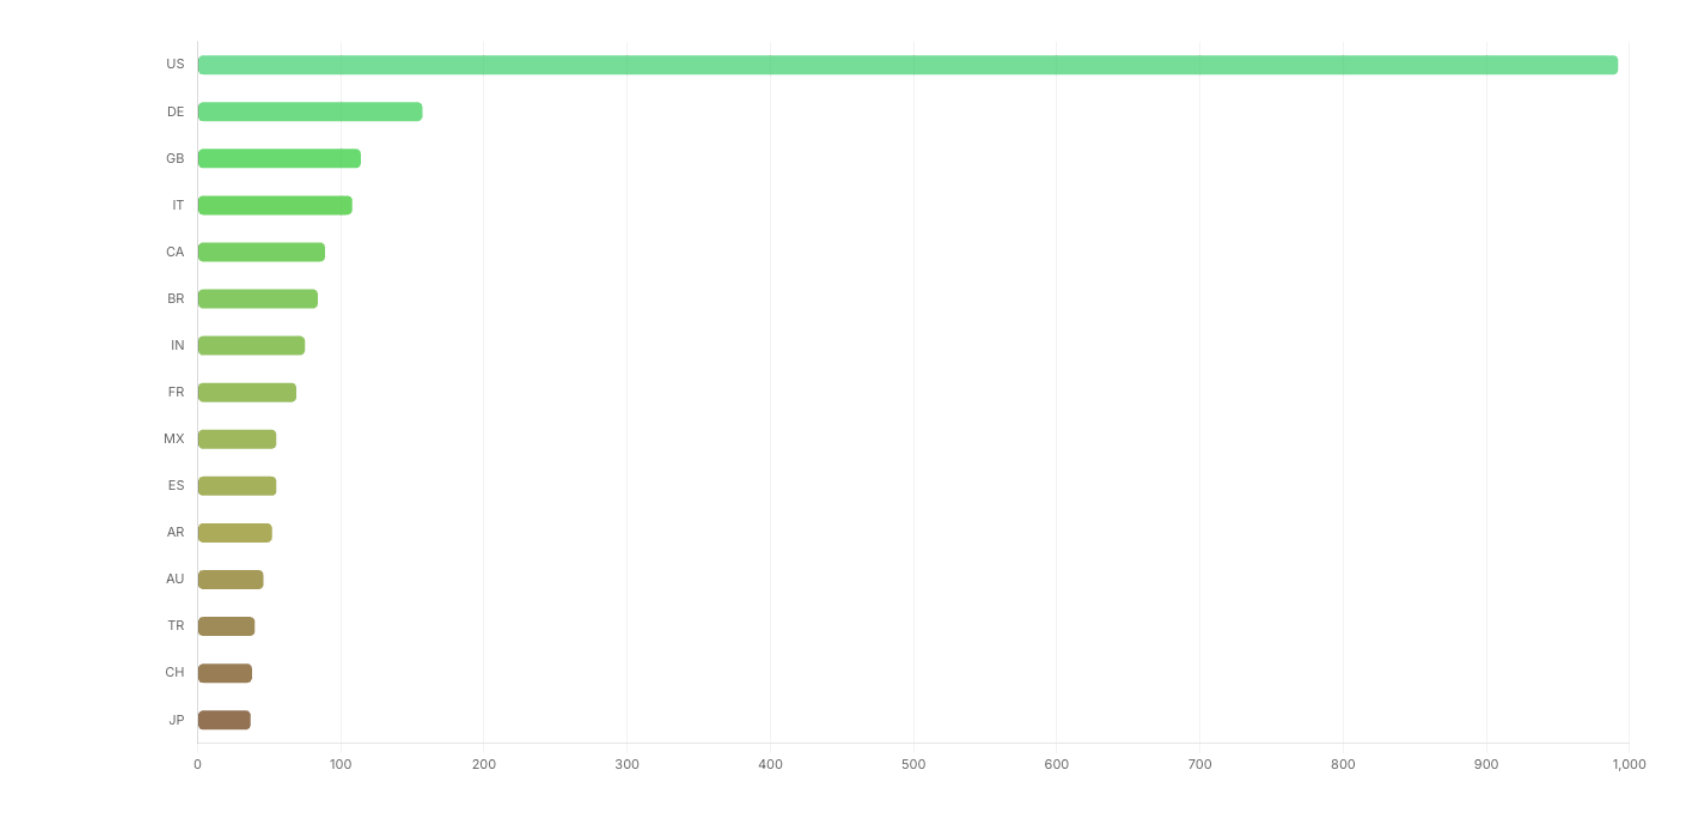
The United States remained the most heavily represented country by a substantial margin. Germany, the United Kingdom, Italy, Canada and Brazil formed the next tier, while India also appears among the leading countries in the quarter's geographic distribution. Of 2,942 Q3 victims, 2,714 were geolocated in the telemetry.
2. Q3 vs Q2: What Changed?
The Q2-to-Q3 comparison points to both scale and diversification. Victim count increased by 569 victims, while 17 additional groups became active. The count of countries affected rose by 17, but the number of represented sectors remained unchanged at 13 — indicating broader geographic and actor expansion rather than expansion into entirely new industry categories.
Q2 was led by Professional Services (519), Manufacturing (394), Technology (260), Retail & E-Commerce (212) and Healthcare (204). By Q3, Manufacturing had moved into first place and Technology and Healthcare had grown substantially, while Professional Services declined.
At the actor level, Qilin led Q2, followed by TheGentlemen and DragonForce. In Q3, TheGentlemen moved to the top position, Qilin remained a dominant operator, and newer/high-growth names such as Krybit and Storm became more visible.
3. New and Emerging Ransomware Groups
CyberMon DRI telemetry identified 34 ransomware brands first seen during Q3, compared with 24 in Q2. The Q3 cohort included Doommageddon, Booba Project, CRPxO, Global Secret Group, ExfilSquad, Orova, Panzer, Dark Project, L Group, Storm, Emperador, Vexy Ransomware, N0n, EndZone and others. The large number of first-seen brands reinforces a recurring challenge for defenders: brand churn can outpace traditional static blocklists and reputation-based monitoring.
Storm stands out within the first-seen Q3 cohort with 76 victims in the quarter's telemetry. Global Secret Group recorded 48, Orova 47, CRPxO 37, Panzer 35, Emperador 32 and Dark Project 30. These counts show that a newly observed brand can establish meaningful victim volume quickly.
4. India Focus
The India-specific dataset contains 75 victims across the full quarter.
India sector profile
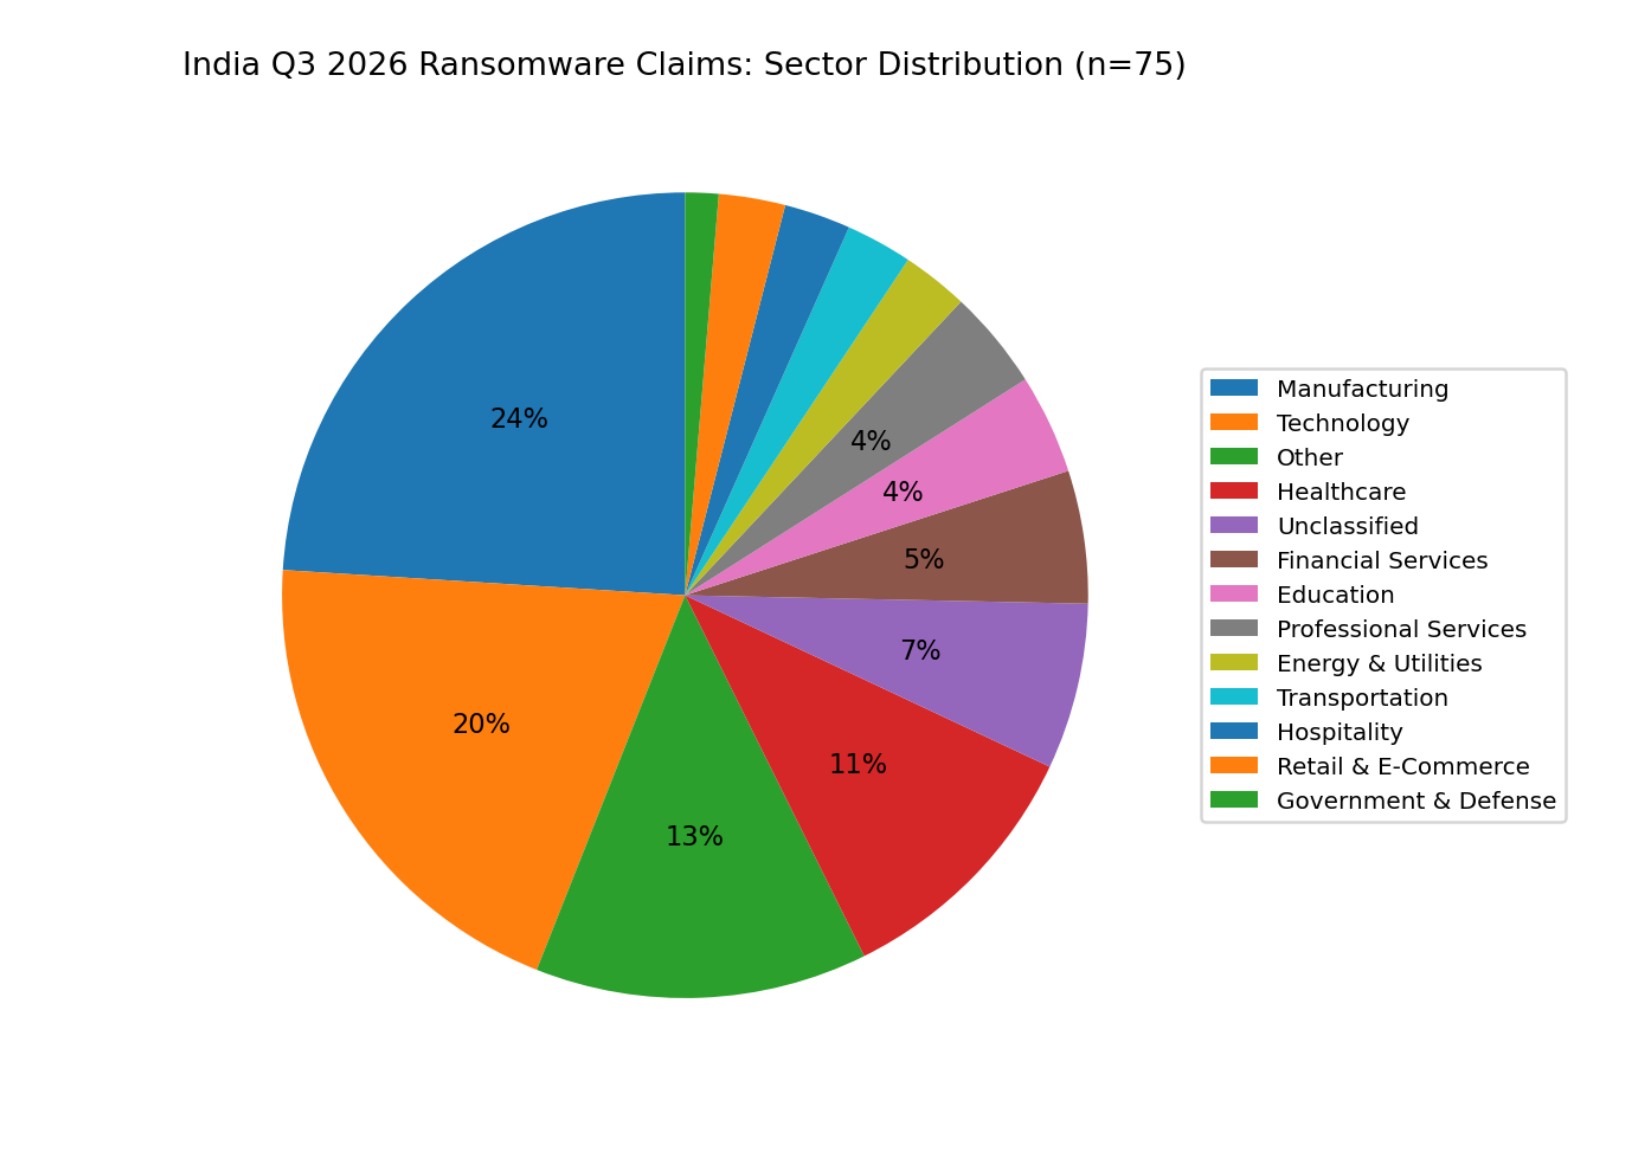
Manufacturing is the largest sector in the India dataset with 18 victims (24.0%), followed by Technology with 15 (20.0%). Other activity accounts for 10 victims (13.3%), Healthcare for 8 (10.7%), Unclassified for 5 (6.7%) and Financial Services for 4 (5.3%). Education and Professional Services record 3 victims each, while Energy & Utilities, Transportation, Hospitality and Retail & E-Commerce record 2 each; Government & Defense records 1.
Top ransomware groups targeting India
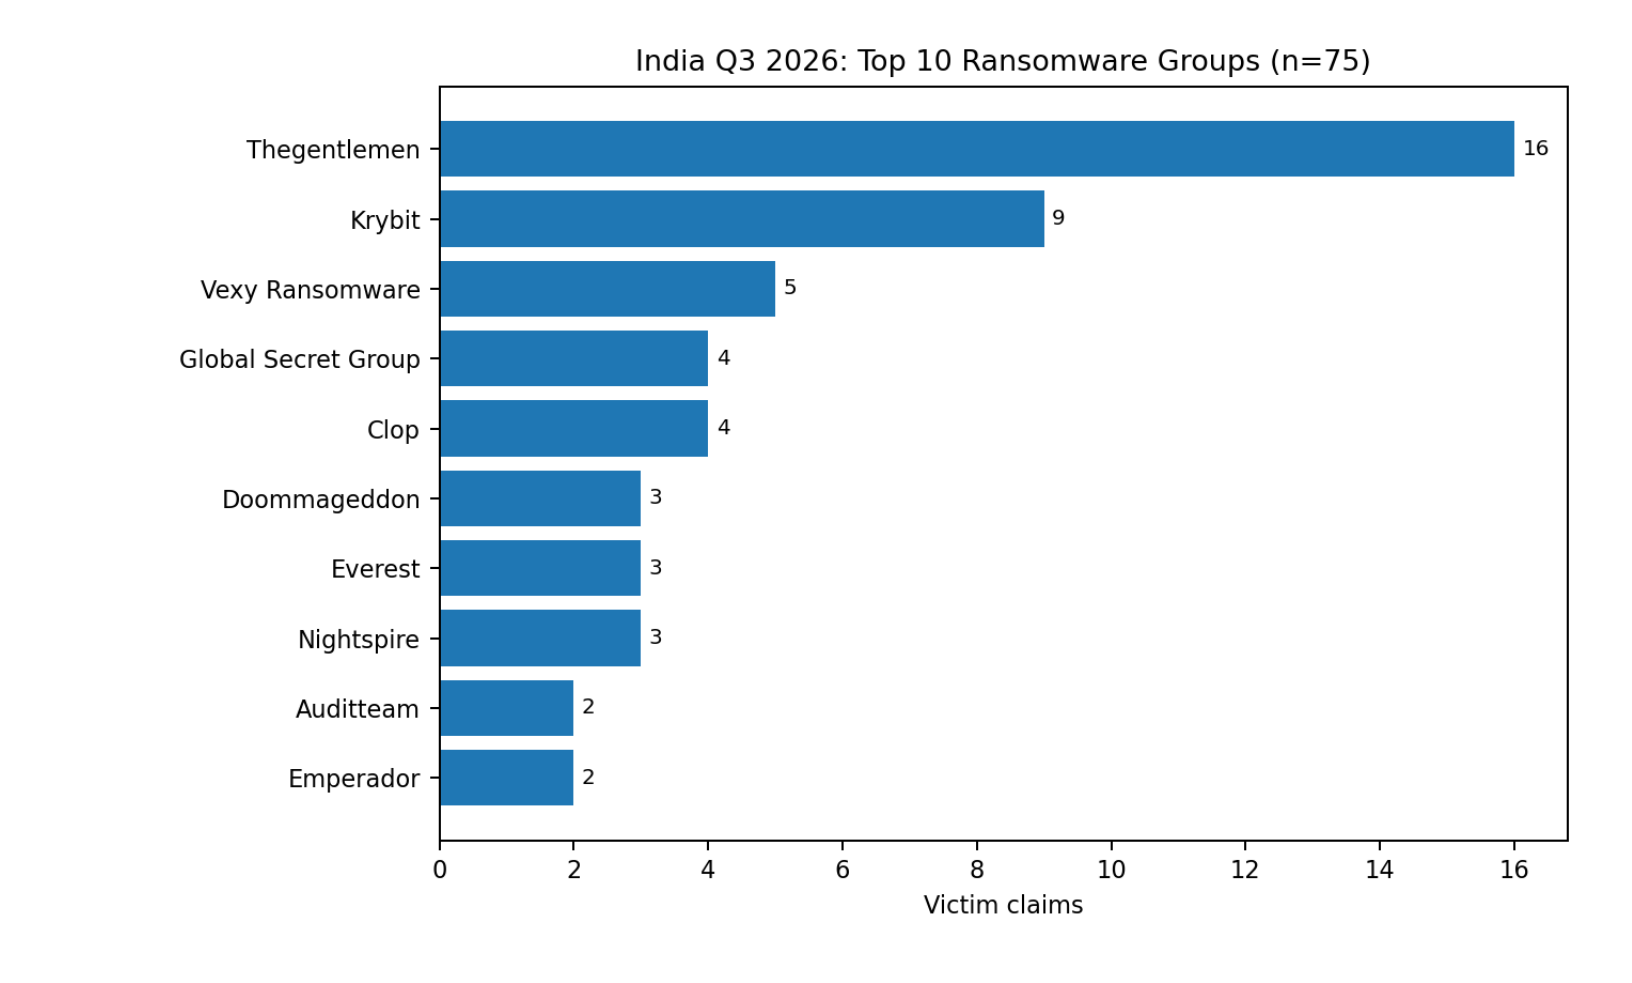
TheGentlemen leads India-focused ransomware activity with 16 victims (21.3%), followed by Krybit with 9 (12.0%) and Vexy Ransomware with 5 (6.7%). Global Secret Group and Clop record 4 victims each, while Doommageddon, Everest and Nightspire record 3 each. Vexy's position remains notable because it was first observed during Q3 yet already ranks third in the India dataset.
Month-wise India listings
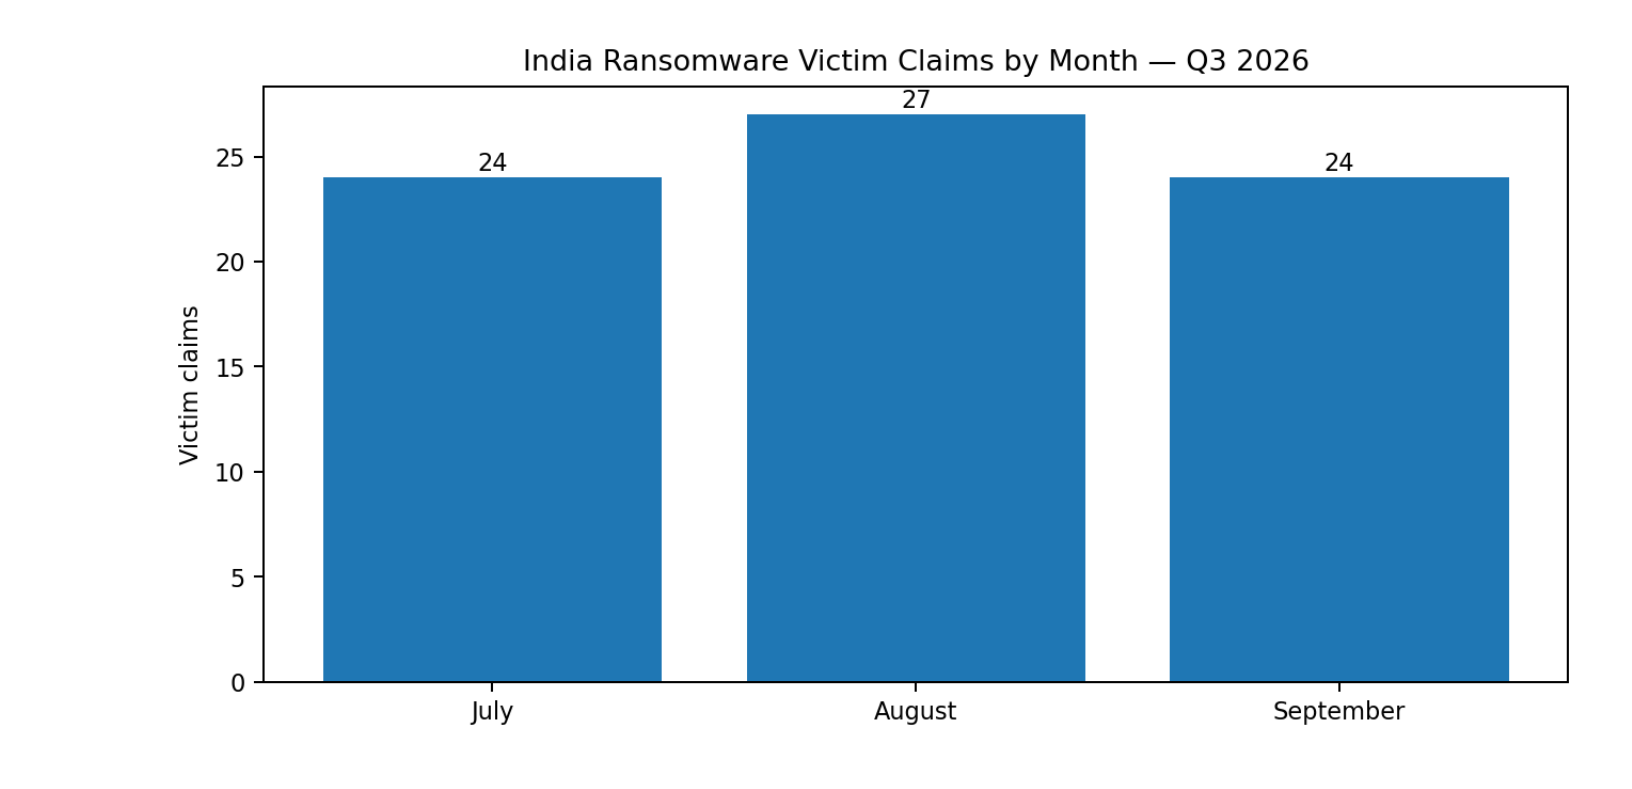
India-focused ransomware activity was remarkably even across Q3: July recorded 24 victims, August 27 and September 24. August was the quarter's highest month, but only marginally, suggesting sustained rather than isolated ransomware pressure on Indian organisations.
India ransomware victim claims list, Q3
The full list of India-geolocated claims observed in Q3, as captured in CyberMon DRI telemetry. Entries are publicly observed leak-site or extortion claims; inclusion here does not independently confirm that a listed organisation was compromised, nor the scope of any compromise.
| Date | Victim | Group | Sector |
|---|---|---|---|
| 2026-09-28 | Chem Process Systems Pvt. Ltd. | Doommageddon | Manufacturing |
| 2026-09-22 | vit.ac.in | Auditteam | Education |
| 2026-09-20 | Siddhi Green Excellence Pvt. Ltd | Orova | Energy & Utilities |
| 2026-09-15 | Indic | Thegentlemen | Technology |
| 2026-09-15 | BGR Energy Systems | Thegentlemen | Energy & Utilities |
| 2026-09-13 | vi***in | Auditteam | Transportation |
| 2026-09-13 | INCOR Group | Doommageddon | Other |
| 2026-09-12 | Nexbex Solutions Private Limited | Emperador | Unclassified |
| 2026-09-12 | swadeshicipl.com | Krybit | Manufacturing |
| 2026-09-12 | Praveg Caves Jawai | Medusalocker | Hospitality |
| 2026-09-10 | CO-OP URBAN BANK LTD | Global Secret Group | Financial Services |
| 2026-09-10 | i2k2 Networks | Vexy Ransomware | Technology |
| 2026-09-09 | Universal Starch-Chem Allied Ltd | Emperador | Manufacturing |
| 2026-09-07 | Soni Dwarkadas Virchand | Thegentlemen | Other |
| 2026-09-07 | United Group | Vexy Ransomware | Other |
| 2026-09-06 | Sancity | Vexy Ransomware | Other |
| 2026-09-04 | Palsana Enviro (PEPL) | Vexy Ransomware | Manufacturing |
| 2026-09-04 | Annapurna Fashion | Vexy Ransomware | Retail & E-Commerce |
| 2026-09-02 | part1.simplexengg.in | Eclipse | Technology |
| 2026-09-02 | Seasia Infotech | Thegentlemen | Technology |
| 2026-09-02 | Licindia | Medusalocker | Other |
| 2026-09-01 | seashellhospital.com | Krybit | Healthcare |
| 2026-09-01 | vedantaainstitute.in | Krybit | Education |
| 2026-09-01 | southsign.in | Krybit | Professional Services |
| 2026-08-31 | R L Fine Chem Pvt. Ltd. | Global Secret Group | Manufacturing |
| 2026-08-30 | G R Infraprojects | Thegentlemen | Manufacturing |
| 2026-08-26 | karkinos.in | Krybit | Healthcare |
| 2026-08-26 | jindallifescience.com | Krybit | Healthcare |
| 2026-08-26 | Simplex Engineering | Eclipse | Manufacturing |
| 2026-08-23 | AGS Cinemas | Thegentlemen | Hospitality |
| 2026-08-21 | Gindre India | Qilin | Manufacturing |
| 2026-08-20 | The University of Delhi (DU) | Dysphor1a | Education |
| 2026-08-16 | BONJOUR GROUP | Majinahanashi | Other |
| 2026-08-15 | DodoPayments | Direwolf | Financial Services |
| 2026-08-15 | www.shalina.com | Blackwater | Unclassified |
| 2026-08-12 | QCPL.IN | Clop | Manufacturing |
| 2026-08-12 | 9ALTITUDES.COM | Clop | Technology |
| 2026-08-12 | ATOMBERG.COM | Clop | Manufacturing |
| 2026-08-12 | JPMGROUP.CO.IN | Clop | Financial Services |
| 2026-08-12 | labindia.com | Krybit | Healthcare |
| 2026-08-10 | DECK APP TECHNOLOGIES PTE. LTD | Unsafe | Technology |
| 2026-08-10 | RAK Construction | Thegentlemen | Manufacturing |
| 2026-08-10 | Lancesoft India | Thegentlemen | Technology |
| 2026-08-07 | ATMS | Incransom | Transportation |
| 2026-08-07 | ratnasagar.com | L Group | Unclassified |
| 2026-08-05 | udhaiyamdhall.com | Orion | Retail & E-Commerce |
| 2026-08-05 | Nitrex Chemicals India | Orion | Manufacturing |
| 2026-08-05 | Greenbotz | Everest | Technology |
| 2026-08-05 | Aptara | Everest | Professional Services |
| 2026-08-05 | Powerweave | Everest | Manufacturing |
| 2026-08-03 | pcclimitedindia.com | Lockbit5 | Manufacturing |
| 2026-07-30 | Delkart Industries Pvt | Thegentlemen | Manufacturing |
| 2026-07-30 | ETA Technology Pvt | Thegentlemen | Technology |
| 2026-07-30 | Kontact Consortium India Pvt | Thegentlemen | Other |
| 2026-07-30 | Indus Protech Solutions | Thegentlemen | Technology |
| 2026-07-27 | K. Venkatesh, Co | Nightspire | Unclassified |
| 2026-07-27 | Wings Argo Private Limited | Nightspire | Other |
| 2026-07-26 | Hinduja Tech | BMW Group & Škoda Auto | Global Secret Group | Manufacturing |
| 2026-07-26 | Cipher Dynamics | Global Secret Group | Technology |
| 2026-07-25 | Principle Diagnostics Laboratory | Qilin | Healthcare |
| 2026-07-24 | Jiva Health | Unsafe | Healthcare |
| 2026-07-24 | Bank of Baroda (bankofbaroda.bank.in) | Triple X | Financial Services |
| 2026-07-23 | origins ivf | Killsec | Healthcare |
| 2026-07-23 | Tikona Infinet | Thegentlemen | Technology |
| 2026-07-23 | DayNDay | Thegentlemen | Other |
| 2026-07-22 | dhli.in | Krybit | Unclassified |
| 2026-07-22 | Vibonum Technologies Private Limited | Krybit | Technology |
| 2026-07-21 | Pertinent Healthcare Business Solutions Private Limited | Titan | Healthcare |
| 2026-07-14 | Omax Autos | Dragonforce | Manufacturing |
| 2026-07-13 | Webosphere | Nightspire | Technology |
| 2026-07-10 | Abhay Prabhavana | Deadlock | Other |
| 2026-07-07 | CSIR Structural Engineering Research Centre | Thegentlemen | Government & Defense |
| 2026-07-06 | Hansa Research Group Pvt. Ltd | Morpheus | Professional Services |
| 2026-07-06 | Innovano | Doommageddon | Technology |
| 2026-07-01 | CTM India Limited (Motherson) | Thegentlemen | Manufacturing |
5. What the Q3 Trend Means for Defenders
- External exposure needs continuous monitoring. The combination of higher victim volume and more active groups increases the probability that exposed internet-facing assets, leaked credentials and forgotten infrastructure are discovered and operationalised by different actors.
- Actor-name monitoring alone is insufficient. Thirty-four first-seen brands in one quarter means defenders should track infrastructure, victimology, credential exposure, initial-access patterns and leak-site activity — not only known ransomware names.
- Manufacturing and technology require heightened attention. Both sectors increased materially from Q2 to Q3, and manufacturing became the largest sector in the quarter.
- India-focused intelligence should be treated as a dedicated lens. The visible India victim list spans manufacturing, technology, education, energy, finance, healthcare and other sectors, with both established and newly observed groups represented.
Methodology and Caveats
This report analyses CyberMon DRI ransomware claim telemetry captured for Q2 and Q3 2026. A "victim" is a publicly observed ransomware/extortion claim; it does not independently prove encryption, payment, or the full scope of compromise. Claim dates represent observed disclosure timing and may differ from intrusion dates. Group counts reflect names/brands present in the telemetry and may include rebrands, splinters or affiliate-driven operations.